
How to Write a NDA for a IT Consulting Company
Learn how to write a NDA for a IT consulting company that protects assessment findings, architecture roadmaps, and vendor evaluations before any engagement begins.

How waxTable generates your IT consulting NDA
- 1
Describe the engagement
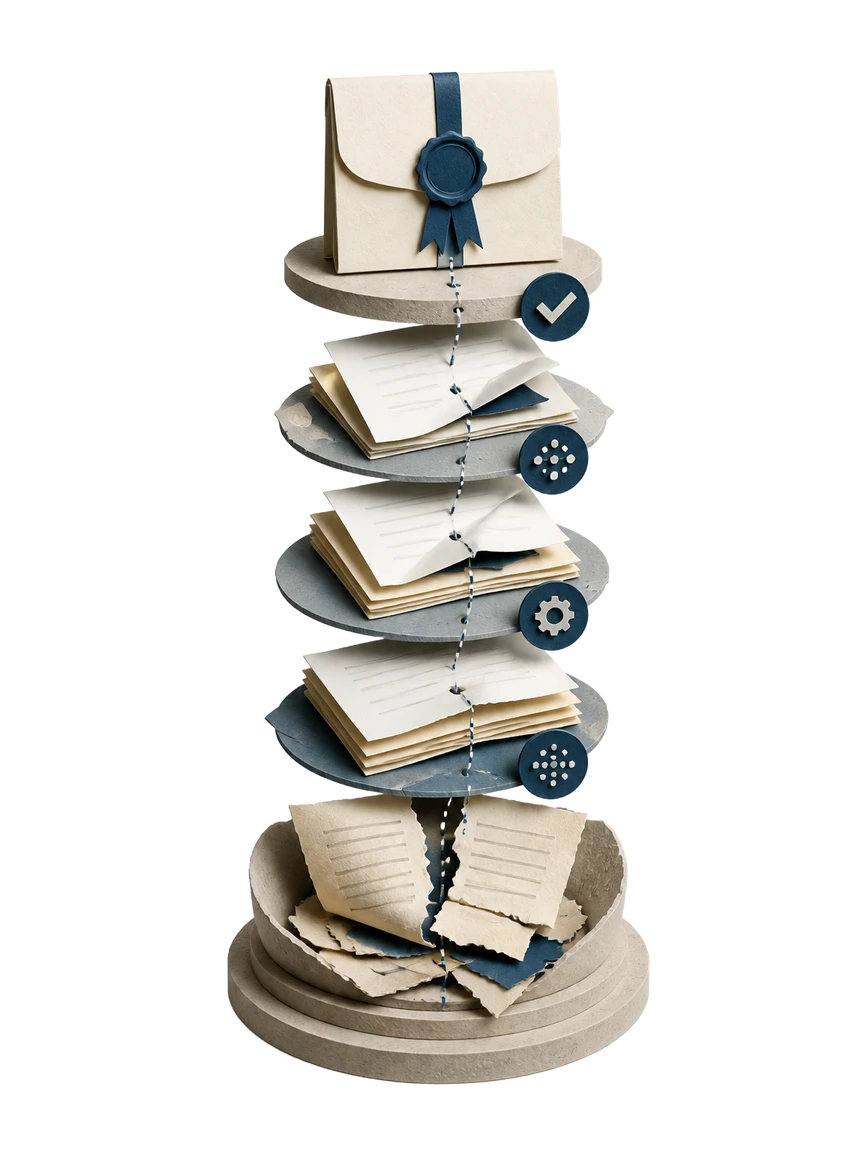
Tell waxTable who the parties are and what the engagement covers, from current-state assessment through managed-support handover. Waxe uses the scope to decide what confidential information the agreement needs to protect. No blank page, no clause hunting.
- 2
Scope the confidential information
Waxe writes the definition around your real deliverables: audit results, target-state architecture, the phased roadmap, and vendor evaluation criteria. This is where most agreements are too vague. Here the protected material is named to match what you actually hand over.
- 3
Set obligations and exclusions
The draft spells out the receiving party's duty to protect, use, and limit access to the material, then adds the four standard exclusions. That balance keeps the agreement enforceable while leaving your reusable methods and reference architectures yours to carry to the next client.
- 4
Pin the term, survival, and remedies
Waxe sets both clocks, the active term and how long confidentiality survives, and writes remedies with governing law in plain language. Roadmap and architecture decisions stay sensitive long after a phase closes, so survival is drafted to outlast the engagement, not expire with it.
- 5
Review, adjust, and send
You read a finished draft with all seven parts in order and change anything before it goes out. Durations, governing state, and named deliverables are yours to tune. The full pass replaces two days of drafting with about five minutes for a few cents.
What goes into a NDA
- 1Parties & purpose
Parties and purpose names the IT consulting firm and the client and states why confidential information is being shared for the engagement.
- 2Definition of confidential information
Definition of confidential information lists exactly what is protected: assessment data, technology audit results, target-state architecture, the roadmap, and vendor evaluation criteria.
- 3Obligations of the receiving party
Obligations of the receiving party set the duty to protect the material, limit who can access it, and use it only for the engagement.
- 4Exclusions from confidentiality
Exclusions from confidentiality carve out information that is public, already known, independently developed, or rightfully received from a third party.
- 5Term & survival
Term and survival sets how long the agreement is active and how long the duty to protect roadmaps and architecture decisions outlives it.
- 6Return or destruction of materials
Return or destruction of materials defines what happens to audit files, run-books, and handover documents when the engagement ends.
- 7Remedies & governing law
Remedies and governing law states the consequences of a breach and which jurisdiction's law governs the agreement.
What's included in your IT consulting NDA
- Parties and purpose written for the consulting firm and client
- Definition of confidential information scoped to your deliverables
- Receiving-party obligations covering use and access limits
- The four standard confidentiality exclusions
- Term and survival with both clocks set explicitly
- Return-or-destruction clause for audit files and run-books
- Remedies and governing-law section in plain language
- Plain-language wording a non-technical executive can sign
The old way versus waxTable
Why IT consulting firms use waxTable for their NDA
Protects what you actually expose
Discovery and assessment hand over audit data, architecture, and vendor scoring before any contract is signed. waxTable scopes the confidential-information definition to those exact deliverables, so nothing you share during the engagement falls outside the agreement.
Minutes instead of days
Drafting a confidentiality agreement clause by clause for each client can consume most of a day. waxTable produces a complete draft with all seven parts in order in about five minutes for a few cents, before the engagement work begins.
Keeps your method yours
You reuse reference architectures and evaluation criteria across clients. The four standard exclusions are written in so a blanket confidentiality claim can't lock up the repeatable advisory method you carry to the next engagement.
Signs without legal back-and-forth
Non-technical executives stall on dense, acronym-heavy clauses. waxTable frames parties, obligations, and remedies in plain language, so the CTO and CFO read the same clear draft and the agreement signs faster.
Consistent across every engagement
Day-rate phases and retainer engagements both start with the same protections. Waxe produces an agreement with the same structure each time, so survival clocks, exclusions, and return clauses never get dropped from one client to the next.
Our promise
An IT consulting NDA has to protect the assessment, the architecture, and the vendor scoring you reveal before the contract is signed. I scope the confidential-information definition to those deliverables and set both clocks so nothing important is left open-ended.Waxe, your AI operations manager
Questions, answered
How to write a NDA for a IT consulting company without a lawyer drafting every line?
Start with the seven parts every confidentiality agreement needs: parties and purpose, what counts as confidential, the receiving party's obligations, the standard exclusions, term and survival, return or destruction of materials, and remedies with governing law. Describe your engagement to waxTable and Waxe generates a complete draft with each part in place. Because IT consulting exposes current-state audits, target-state architecture, and vendor scoring before a contract is signed, the definition of confidential information is written to cover exactly that work. You review and adjust, rather than start from a blank page. The whole pass takes about five minutes for a few cents.
What should the definition of confidential information cover for an IT consulting engagement?
It should name the specific deliverables you expose during discovery, not just "all information." For an IT consulting firm that means current-state assessment data, technology audit results, target-state architecture, the implementation roadmap, vendor and platform evaluation criteria, and any risk, security, or compliance findings. waxTable writes the definition around what you actually deliver, so a client cannot later claim your assessment method or vendor scoring was never protected. It also leaves room for the run-book and managed-support handover details that change hands late in the engagement. Vague definitions are the gap most break-fix-style agreements miss.
How long should the duty to protect confidential information survive after the engagement ends?
The term and survival clause sets two clocks: how long the agreement is active and how long the confidentiality duty outlives it. IT consulting roadmaps and architecture decisions stay sensitive long after a phase closes, so survival is usually set well past the active term. waxTable drafts both clocks explicitly and ties survival to the kind of material you handle, rather than leaving it open-ended or silent. You decide the exact durations; Waxe makes sure neither clock is missing. Open-ended silence here is what invites scope and disclosure disputes later.
What are the standard exclusions from confidentiality, and why do they matter here?
Exclusions carve out information that was already public, already known to the receiving party, independently developed, or rightfully received from a third party. They matter for IT consulting because you reuse general methods, reference architectures, and evaluation criteria across clients, and you need that knowledge protected from a blanket confidentiality claim. waxTable writes the four standard exclusions so your repeatable advisory method stays yours. This keeps the agreement enforceable instead of overreaching. A NDA that claims everything is confidential tends to protect nothing when tested.
How does the NDA help a non-technical client understand what they're signing?
Executives signing the agreement are often non-technical, so plain language matters more than acronyms. waxTable frames the parties, purpose, and obligations in clear sentences that say what is being shared and what each side must do with it. The remedies and governing-law section spells out consequences without legal density. Because the same draft reads cleanly for a CTO and a CFO, the agreement signs faster and raises fewer questions. That clarity is the same reason your proposal reads as strategic advisory rather than a price list.
Your next NDA, in five minutes
Tell Waxe about the client and get a complete, on-brand NDA to review — the work of two days for a few cents. There is no blank page to start from and nothing to format by hand; you answer a short brief, Waxe does the drafting, and you keep full control of the final document in the editor.