
AI Requirements Document Generator for IT Consulting
An AI Requirements Document Generator for IT Consulting that turns discovery notes into a testable, ID-stamped spec in minutes for a few cents.

Built for IT Consulting
Where it hurts
- Buyers can't tell a strategic advisory engagement apart from cheap break-fix support when the proposal reads like a price list
- Open-ended discovery and assessment work invites scope creep unless phases and decision gates are pinned down
- Non-technical executives need the business case and risk framed in plain language, not a stack of acronyms
- Recommending a platform or vendor raises trust questions the proposal has to answer with method, not opinion
- Day-rate or retainer pricing looks expensive next to a fixed quote until the value and outcomes are made explicit
Pricing model: day-rate phases or monthly retainer
What you hand over
- Current-state assessment and technology audit
- Target-state architecture and roadmap
- Vendor and platform selection with evaluation criteria
- Implementation plan with phases and milestones
- Risk, security and compliance review
- Change management and staff enablement
- Run-book and managed-support handover
What goes into a Requirements Document
- 1Overview & objectives
Overview and objectives frames the engagement and its business case in plain language an executive sponsor can read without an acronym glossary.
- 2Scope & context
Scope and context pins the boundary of the current-state assessment and target-state work so discovery cannot quietly expand.
- 3Functional requirements
Functional requirements list each capability the solution must perform as a single verifiable statement with a stable ID.
- 4Non-functional requirements
Non-functional requirements capture performance, security, compliance and reliability limits as testable statements, not vague intentions.
- 5Acceptance criteria
Acceptance criteria attach a checkable pass condition to each requirement so sign-off is evidence, not opinion.
- 6Assumptions & constraints
Assumptions and constraints record the conditions, dependencies and platform limits the recommendation and roadmap rely on.
- 7Out-of-scope
Out-of-scope names everything the engagement deliberately excludes, turning every later request into a change order rather than a dispute.
How Waxe builds your requirements document
- 1
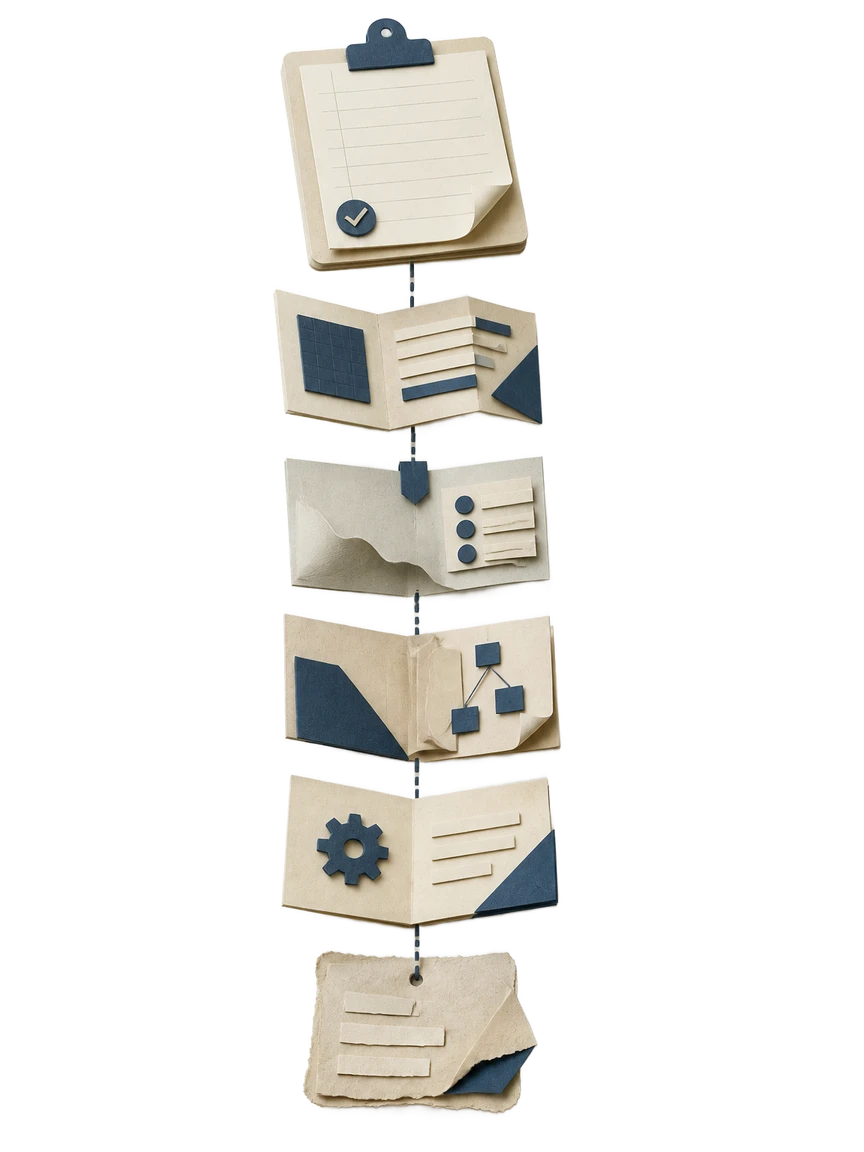
Share your discovery notes
Drop in the findings from your current-state assessment and technology audit, plus the client's goals and any compliance limits. Waxe reads it all and pulls out the objectives, capabilities and constraints worth specifying. No template to fill in first.
- 2
Waxe drafts testable requirements
Waxe writes each functional and non-functional requirement as a single verifiable statement and assigns a stable ID. Every requirement gets matching acceptance criteria. Assumptions and constraints are captured alongside, so the spec is reviewable the moment it appears.
- 3
Set scope and the out-of-scope line
You confirm what the engagement covers and what it explicitly does not. Waxe pins phases and decision gates into the scope section and lists exclusions plainly. This is the boundary that keeps open-ended assessment work from sprawling later.
- 4
Apply your firm's voice and brand
Waxe designs the document in your house style, keeping the overview readable for executives while the requirements stay exact for engineers. Headings, colour and layout match the rest of your proposal set. The output looks like your firm, not a generic form.
- 5
Review, edit and export
Walk the draft, adjust any requirement or acceptance criterion, and approve. Waxe regenerates clean in moments, so a document that took two days by hand is ready in about five minutes for a few cents. Export and send.
What an on-brand requirements document looks like
The result opens with objectives a sponsor can read, then moves into ID-stamped functional and non-functional requirements, each paired with acceptance criteria. Scope, assumptions and an explicit out-of-scope section bracket the work. It carries your firm's colours and type, so it reads as a deliverable, not a filled-in form.
The old way versus waxTable
Why IT consulting firms use it
Requirements you can verify
Every functional and non-functional requirement is a single testable statement with a stable ID. Acceptance criteria make each one checkable. Reviews stop being debates and become confirmations against written conditions.
Scope creep loses its opening
Explicit scope, assumptions and an out-of-scope section pin the boundary of discovery and assessment work. Phases and decision gates are spelled out. When a request lands outside the line, the document is your reference for a change order.
Trust by method, not opinion
Vendor and platform recommendations rest on evaluation criteria drawn from the requirements themselves. Constraints capture the security and compliance limits. The selection reads as an auditable method, which protects your firm if it is later questioned.
Readable for executives, exact for engineers
Objectives and the business case appear in plain language without an acronym wall. Underneath, the requirements stay precise enough to build from. One document serves the sponsor signing it and the team delivering it.
Two days of work in minutes
Waxe turns discovery notes into a complete, ID-stamped specification in about five minutes for a few cents. You review and approve instead of formatting from scratch. The time goes back into the advisory work clients actually pay for.
Questions, answered
What does the AI Requirements Document Generator for IT Consulting actually produce?
It produces a precise specification where every requirement is a single verifiable statement with a stable ID. The document opens with overview and objectives, pins down scope and context, then separates functional from non-functional requirements. Each requirement carries acceptance criteria a reviewer can check against. Assumptions, constraints and an explicit out-of-scope section close the gaps that invite scope creep. Waxe drafts the whole structure from your discovery notes, so you edit and approve rather than format from scratch.
How does this help a strategic engagement read differently from cheap break-fix support?
A price list makes advisory work look interchangeable with hourly fixes. This document leads with objectives and a target-state framing, then ties every functional and non-functional requirement to a verifiable outcome. The acceptance criteria show what success looks like before any day-rate phase begins. Buyers see method and scope, not just a number. That distinction is what justifies day-rate phases or a monthly retainer against a low fixed quote, and it does the framing for you.
Can it keep open-ended discovery and assessment work from sprawling?
Yes, and that is the point of the scope, assumptions and out-of-scope sections. Discovery, technology audits and target-state architecture all invite scope creep when the boundary is vague. Waxe forces an explicit out-of-scope list and pins assumptions and constraints alongside each requirement. Phases and decision gates become readable, so the client signs off on exactly what each phase covers. When a request lands outside that line, the document is your reference for a change order rather than an argument.
Will non-technical executives understand a requirements document this detailed?
The overview and objectives section is written in plain business language, framing the case and risk without a stack of acronyms. Functional requirements stay precise for engineers, while the objectives and acceptance criteria translate them into outcomes an executive sponsor can weigh. The risk, security and compliance angle appears as constraints rather than jargon. You decide the tone, and Waxe keeps the audience layered: readable up top for decision-makers, exact underneath for the people who build.
How does the document support a vendor or platform recommendation?
Recommending a platform raises a trust question, so the document answers it with evaluation criteria rather than opinion. Functional and non-functional requirements become the measuring stick every candidate vendor is scored against. Constraints capture the security, compliance and integration limits that rule options in or out. Acceptance criteria define what the chosen platform must demonstrably do. The selection then reads as a method the client can audit, which protects your firm if the recommendation is later questioned.
Your next requirements document, in five minutes
Tell Waxe about the client and get a complete, on-brand requirements document to review — the work of two days for a few cents. There is no blank page to start from and nothing to format by hand; you answer a short brief, Waxe does the drafting, and you keep full control of the final document in the editor.